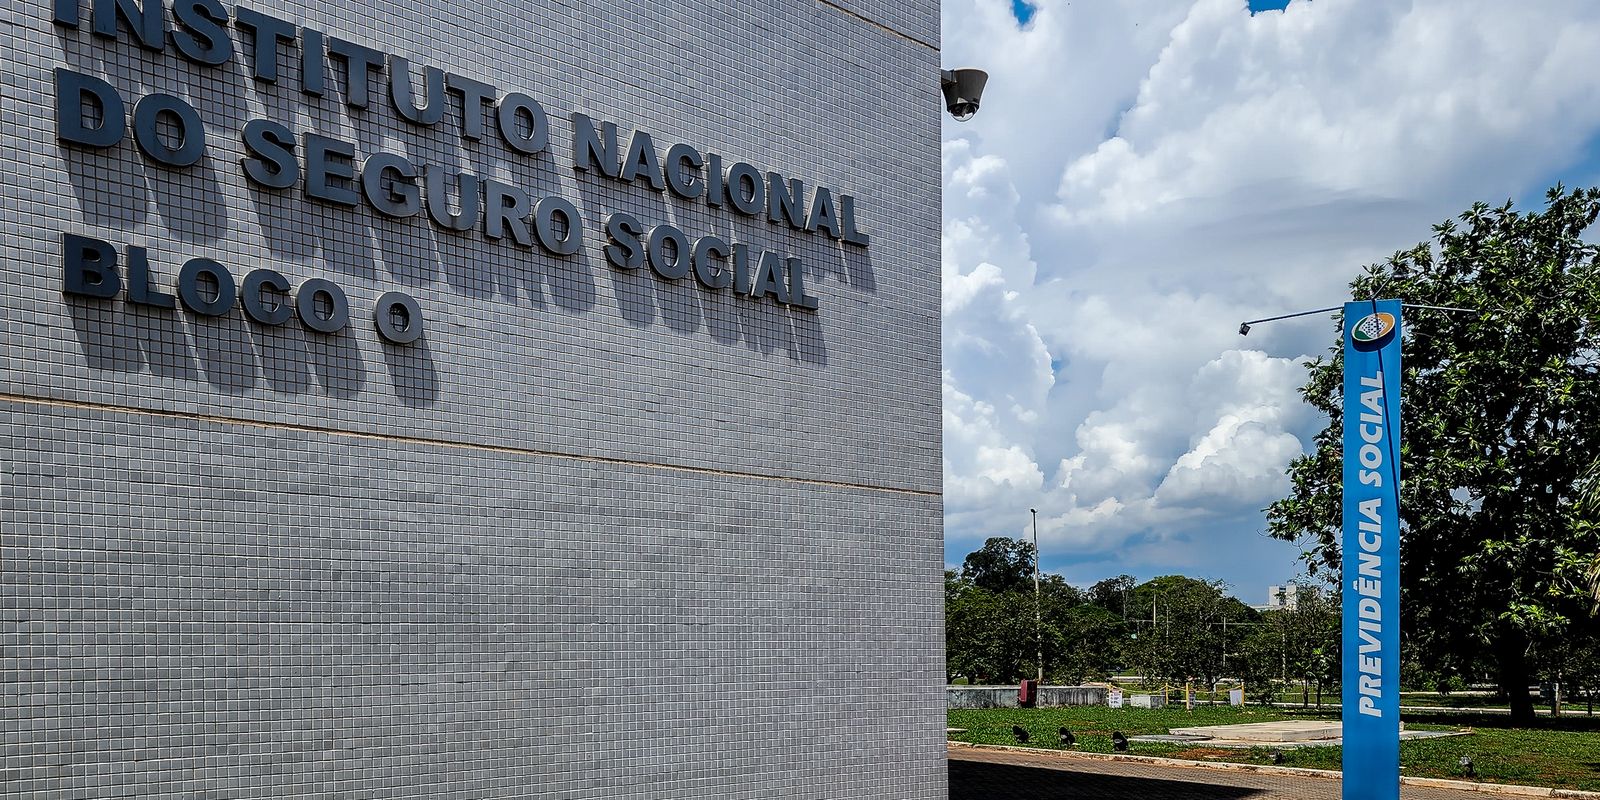
The National Institute of Social Security (INSS) confirmed in a statement that about 40 million pensioners and pensioners had their registration data exposed through unsupervised access. The problem has occurred for decades Logins Of public servants from bodies outside INSS who have retired, been dismissed or resigned.

The agency stressed that the problem did not cause losses to the public treasury because the Unified Benefits Information System (Suibe) is not used to release benefits. The system only stores beneficiary data such as name, individual taxpayer record (CPF), type of benefit (retirement, superannuation, maternity pay, assistance, continuous payment benefits), date of grant and amount received.
According to INSS, in previous administrations, passwords were distributed to other federal agencies to enter the system. It was distributed to oversight bodies, such as the Comptroller General of the Federation and the Attorney General of the Federation, to defend the government in legal cases. However, there was no monitoring of passwords. Access was only via sign in and password, without security layers like two-factor authentication, digital certificate, and encryption.
After third-party employees leave their jobs, Logins The passwords remained valid and could fall into the hands HackersOr fraudsters or criminals. One potential use of external passwords is to sell data to financial institutions that provide payroll loans to beneficiaries. Another possibility is that the criminals, who had the data, requested special credit in the name of the insured by INSS.
Measurements
In the statement, INSS reported that Dataprev, the body that developed the Suibe technology solution, detected an increase in the flow of information requests into the system. The external passwords were immediately suspended, and the government established a protocol to grant access to other federal agencies. External access will now require a digital certificate and encryption.
“A server from some agency that has access to Suibe retires or passes another competition and holds the password. It was not 'unregistered.'” “Now, with the digital certificate and encryption, no one with the password will have access,” INSS highlighted in the memo.
The National Institute of Statistics reported that it is still investigating the impact of disclosing beneficiary data and verifying whether there was indeed a leak of information. The case will not be referred to the federal police until analyzes are completed.
“Suíbe was the first INSS data extraction system to which the access flow was changed by the new technological security rules, which are being renewed in 2024. The systems that generate the granting of benefits already have a new layer of security,” highlights the statement.
Close statistics
Before adding layers of security to Suibe, INSS shut down the system in early May. The temporary shutdown paralyzed the production of statistics, such as the Social Security Statistical Bulletin (Beps).
With detailed information about granting and paying benefits, Beps is based on Suibe data. The latest version of the report was released in February this year.
Charlotte Whitmore is a contributor at Mediarunsearch.co.uk, covering a broad range of topics including news, politics, business, technology, sport, entertainment, and lifestyle. She focuses on delivering clear, balanced reporting and practical information that helps readers stay informed about current events and emerging developments. Her work highlights stories that matter to everyday audiences, with an emphasis on accuracy, relevance, and accessible journalism that keeps readers connected to the issues shaping the UK and beyond.